Data Access Governance Tools: Top Vendors Compared in 2026
Key Takeaways: Requests to grant access are far more common than directiv...


____________
An AI prompt box looks like a search bar, and people treat it like one.
Typing into an AI assistant feels closer to thinking out loud than to moving company data somewhere new. Copilots and agents then add their own traffic on top, retrieving and recombining whatever their inherited permissions allow, at a pace that makes manual review look decorative.
Security teams face tough questions that are becoming increasingly difficult to answer. Which AI tools are employees actually using? What data are those tools accessing? What can a copilot see through the permissions it inherited?
The last question deserves special attention because AI assistants run with whatever access their users already have. Every overshared folder and every stale permission can become something a copilot retrieves in seconds.
“AI security” can describe everything from model integrity to prompt-injection defense. For this comparison, we focus on the layer where most enterprise AI risk concentrates: data. Specifically, we look at the tools that help organizations discover, govern, and protect sensitive data as it flows into and out of AI systems.
At the data layer, AI security is the practice of understanding and controlling how AI tools interact with sensitive data.
That includes what employees share with AI applications, what copilots and agents can access through existing permissions, and what sensitive information ends up in AI-generated output.
In practice, AI security tools aim to answer three key questions:
The concept sounds straightforward, but the reality is more complex. Security teams monitoring dozens of AI applications, thousands of users, and data that was sprawling before AI arrived.
Many AI security deployments look impressive in a demo. The dashboard shows AI usage, a few policy violations light up, and the tool appears to have things handled.
Then employees adopt three new AI apps the vendor has never seen, and an agent framework goes live.
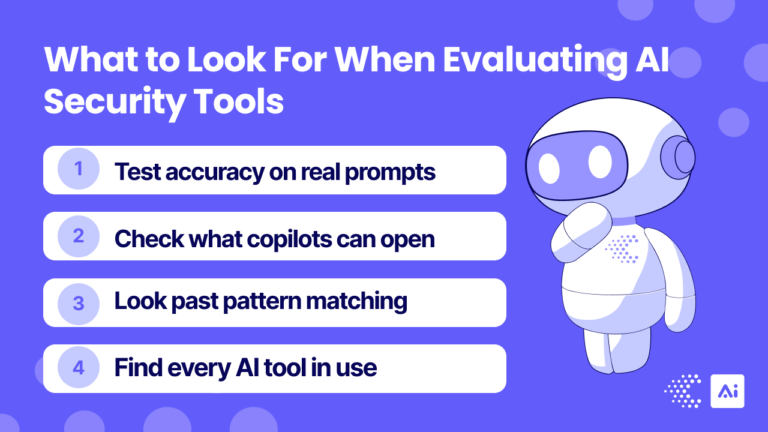
A few areas are worth pressure-testing:
Pro Tip: A tool that only covers the AI applications it knew about at deployment can fall behind within a quarter.
The following vendors all address AI security, but each approaches the problem from a different starting point. That starting point can tell you a lot about where each tool performs best.
Concentric AI applies semantic analysis to identify sensitive data and exposure risks across unstructured environments and AI interactions. It covers tools such as Microsoft Copilot, ChatGPT, Claude, Gemini, and Perplexity.
Microsoft Purview provides a DSPM for AI console that monitors Copilot and third-party AI usage, with policies and auditing that integrate tightly with Microsoft 365.
Spirion approaches AI security through data readiness, focusing on discovering and classifying sensitive data before AI tools can touch it.
Netwrix comes at the problem from the identity side, giving organizations visibility into what AI agents and assistants can access through existing permissions.
Sentra focuses on AI data readiness in cloud environments, mapping which data stores feed AI systems and adding browser-based controls for shadow AI usage.
| Vendor | Where It Stands Out | Potential Tradeoffs | Best Fit For |
|---|---|---|---|
| Concentric AI (Semantic Intelligence) | DSPM and DLP capabilities powered by patented LLMs to understand data context and exposure risk, without relying on rules or pattern matching. Inline categorization, prompt and response monitoring, and warn, block, or redact enforcement | Requires some integration with governance and enforcement tools for full remediation workflows | Organizations that need to uncover, protect, and remediate AI data exposure across large unstructured environments |
| Microsoft Purview | DSPM for AI console with prebuilt policies, Copilot prompt and response auditing, and deep Microsoft 365 integration | Strongest inside the Microsoft ecosystem; effectiveness depends heavily on label and policy configuration; some capabilities are tied to Copilot licensing | Organizations standardized on Microsoft 365 and rolling out Copilot |
| Spirion | Strong data discovery and classification as the preparation step for AI adoption | Approaches AI security through data readiness rather than AI usage monitoring; pattern-based discovery can miss contextual exposure | Organizations that want sensitive data found, classified, and remediated before AI reaches it |
| Netwrix | Identity-centric visibility into what AI agents and Copilot can access through existing permissions across hybrid environments | Views AI risk primarily through the permissions lens, with less depth on prompt-level activity or semantic analysis of unstructured content | Organizations focused on permissions governance ahead of Copilot and agent rollouts |
| Sentra | Cloud-native platform mapping which data stores and knowledge bases feed AI systems, with browser-based shadow AI controls | Primarily focused on cloud data environments rather than broader governance workflows | Cloud-heavy organizations that need to understand which sensitive data their AI systems consume |
For years, even decades, the standard advice for emerging technology risks was to wait for the threat to materialize and then respond.
AI has eliminated that waiting period. The risk is present from day one, mainly because it comes from ordinary employees trying to do their jobs faster.
Think of that folder that was accidentally overshared and then forgotten. It may have sat there for three years, more or less harmless. Then someone asks a copilot for a summary of everything the company knows about a customer, and that folder can spring up in seconds—its contents available to whoever asked. The employee did nothing malicious. The permissions were the problem long before AI arrived.
AI just amplifies the consequences.
That is why AI security continues climbing the priority list:
Organizations can only protect what they can see, and AI has made a lot of data movement invisible.
In the data security context, AI security tools monitor and govern how AI systems interact with sensitive data. They discover which AI applications are in use, identify sensitive content in prompts and files, analyze what AI assistants can access, and flag exposure before it becomes an incident.
Most platforms in this category are built to cover:
The real value comes from connecting these layers, so security teams can see exactly how sensitive data travels through AI workflows.
On paper, most AI security tools describe themselves similarly. The differences become clear when they encounter real prompts, real permissions, and real data sprawl.
Here are the core capabilities to look for:
AI usage discovery
Identify which AI applications employees use, including unsanctioned tools nobody approved.
Sensitive data identification
Detect sensitive content in prompts, uploads, and files that AI tools can access, across structured and unstructured data formats.
Access analysis
Map what copilots and agents can access through inherited permissions and identify where that access is too broad.
Policy enforcement
Warn users, block sharing, or apply protections when sensitive data is sent to an AI tool.
Monitoring and reporting
Track AI interactions over time and help organizations demonstrate compliance as AI regulations evolve.
Together, these capabilities give security teams something they often lacked through the first wave of AI adoption: context.
Adoption in this category tends to be driven by a few consistent needs:
Copilot readiness
Before rolling out Microsoft Copilot or similar assistants, organizations need to find and fix oversharing that a copilot could instantly amplify.
Shadow AI visibility
Security teams need to know which AI applications employees use and what data is flowing into them, without resorting to blanket bans.
Regulatory compliance
As AI-specific regulations emerge alongside existing privacy laws, organizations need to show what data their AI systems access and how that data stays protected.
The common thread is the same one driving DSPM adoption: visibility. AI has just raised the stakes and shortened the timeline.
AI security tools overlap with several established categories, and the boundaries can be confusing for buyers. Each technology solves a different part of the problem.
AI security vs DSPM
DSPM identifies where sensitive data lives and how it is exposed across an environment. AI security at the data layer extends that visibility into AI interactions: the prompts, copilots, and agents now accessing that data. The strongest platforms treat AI as one more environment within a broader data security posture.
AI security vs DLP
DLP focuses on preventing sensitive data from leaving through defined channels. AI security addresses broader questions: What can AI systems access? What are users sharing with them? And what does the generated content contain? The two work best together, with data context strengthening DLP enforcement.
AI security vs model security
A separate discipline focuses on the models themselves: prompt injection, model integrity, and adversarial inputs. These threats are real, but for many enterprises, the more immediate exposure comes from ordinary data flowing into ordinary AI tools without enough oversight.
When generative AI first hit the enterprise, most organizations reached for the tools they had.
The results were predictable:
All four approaches rely on controls built for defined channels and predictable formats. The problem is they’re applied to a technology that respects neither.
Most tools in this category evaluate AI risk by matching patterns or checking labels. That approach can catch the obvious cases while missing the context that determines whether AI activity actually creates exposure.
Powered by the Semantic Intelligence Engine’s patented language models, the platform discovers, governs, and protects business-critical and compliance-sensitive data at rest, in motion, and as it used by AI through a consistent policy framework.
Because Concentric AI understands the actual data context, it can identify sensitive content with a high degree of accuracy across documents, collaboration environments, and AI interactions, including Microsoft Copilot, ChatGPT, Claude, Gemini, and Perplexity.
Instead of simply flagging AI usage, Semantic Intelligence provides clear visibility into:
With this visibility, security teams can support AI adoption rather than fight it. When organizations understand what their AI tools can see—and what their employees are sharing with them—they can enable the business to use AI with confidence.
