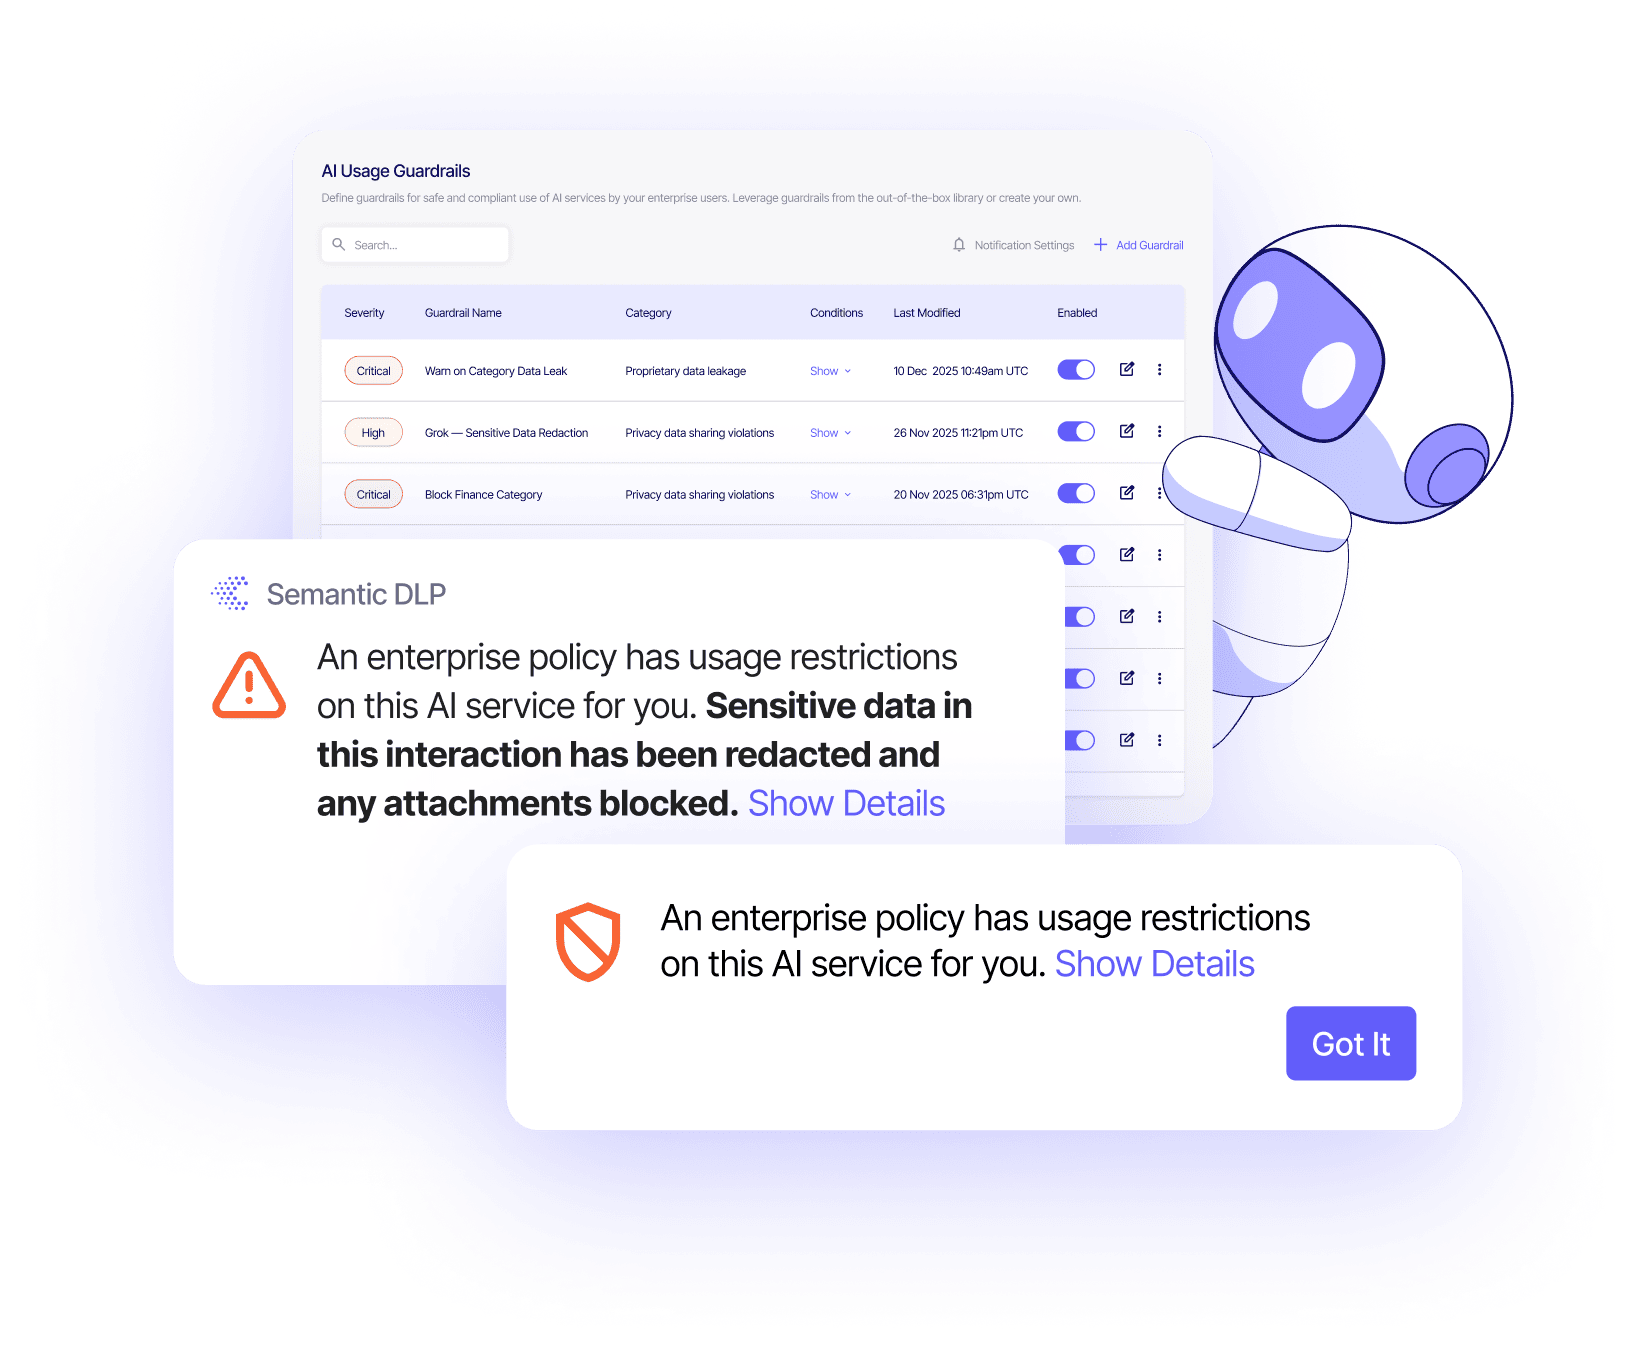
Inspect AI interactions in real time and stop sensitive data from being exposed before it reaches the AI application.
Concentric AI enforces AI policies based on what data means—not just keywords—so security teams can protect sensitive information without blocking productive AI use.
AI interactions move too quickly for manual review. Concentric AI inspects prompts, uploads, and other AI activity in real time, using semantic context to identify sensitive data and apply the right policy before it reaches the AI application.
Security shouldn't have to choose between stopping sensitive data and letting employees use AI productively. Concentric AI gives teams precise enforcement options that protect sensitive data while allowing legitimate AI use to continue.
AI DLP protects sensitive data as it is shared with AI applications. Concentric AI inspects prompts, uploads, and other AI interactions to identify sensitive information and apply policies before data is exposed.
Traditional DLP protects data across established channels such as email, web, and file transfers. AI DLP extends that protection to AI-specific interactions, including prompts and uploads, where users can share sensitive information directly with AI applications.
Concentric AI uses its Semantic Intelligence Engine to understand the meaning and context of data, rather than relying solely on keywords or pattern matching. This helps identify sensitive content more accurately and apply policies with greater precision.
AI DLP inspects AI interactions such as prompts and uploads to identify sensitive information before it is shared with an AI application. Concentric AI also captures prompts, responses, and policy violations, giving security teams visibility into the interaction and the data involved.
Yes. Concentric AI logs prompts, responses, and policy violations to give security teams visibility into AI interactions and the sensitive data involved. Teams can use this information to investigate violations, understand AI usage, and refine policies and controls.
Yes. Organizations can create policies that block sensitive content when it violates established data protection requirements, helping prevent data exposure without blocking legitimate AI use altogether.
Yes. Concentric AI can mask sensitive portions of prompts or uploads while allowing non-sensitive content to continue through, giving users a way to use AI without exposing protected information.
Yes. Policies can be configured to warn users when they are about to share sensitive information, allowing organizations to apply a level of enforcement appropriate to the data and the situation.
Yes. AI DLP can apply data protection policies to interactions with sanctioned, unsanctioned, and emerging public AI applications, helping prevent sensitive information from being shared even when employees adopt tools outside the approved AI ecosystem.
AI DLP focuses on detecting and preventing sensitive data from being shared through AI interactions. AI Data Guardrails provides the broader governance framework for understanding AI and data activity, defining contextual policies, and establishing boundaries for how AI uses sensitive data. The two work together to govern AI use and protect sensitive data.