AI Security Tools: Top Vendors Compared in 2026
Key Takeaways: ____________ An AI prompt box looks like a search bar, and...

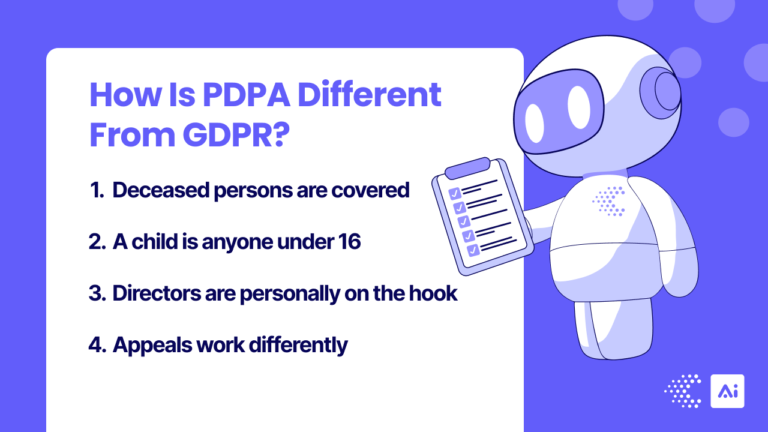

Sri Lanka made history in March 2022 when it became the first country in South Asia to pass a comprehensive data protection law. The Personal Data Protection Act, No. 9 of 2022 (PDPA) established a Data Protection Authority, defined penalties of up to LKR 10 million per violation, and borrowed heavily from the playbook that gave us GDPR.
Four years later, and up until July of 2026, the substantive provisions that most businesses actually care about were waiting on a commencement order in the Government Gazette. That finally changed on July 22, 2026, when Gazette Extraordinary No. 2498/16 set January 1, 2027 as the operational date for Part I (Processing of Personal Data) and Part III (Controllers and Processors), while data subject rights under Part II and the penalty regime under Part VII wait on a further order.
This waiting period has lulled many organizations into treating the PDPA as a problem for a future date, which is a mistake, because when January 1 arrives, the core obligations will be enforceable.
If you’ve worked through GDPR compliance, the PDPA will feel familiar. The lawful bases for processing, purpose limitation, data minimization, retention limits, and breach notification are all there, as well as a rights framework that lets individuals access, correct, and erase their data.
But several provisions distinguish the Sri Lankan data protection act from the European act.
Here are the four that stand out the most.
The PDPA’s reach extends well beyond the capital of Colombo. Section 2 applies the Act to any processing that takes place wholly or partly within Sri Lanka, and to controllers and processors anywhere in the world that offer goods or services to data subjects in Sri Lanka or specifically monitor their behavior, including profiling.
If your SaaS platform has Sri Lankan customers, or if your e-commerce site ships there, or your analytics stack profiles users in the country, you’re in scope. The same geographical rules that pulled global enterprises into GDPR compliance apply here as well, and they’re backed by a government eager to position Sri Lanka as a trusted digital economy.
Cross-border transfers also get their own regime, and it changed substantially in the Personal Data Protection (Amendment) Act, No. 22 of 2025, which replaced Section 26 outright. The adequacy decision mechanism from the 2022 text is gone. Under the amended Section 26, a controller or processor may move personal data abroad only where it complies with Part I, Part II, and Sections 20 through 25, and adopts the safeguard instruments specified by an Authority directive.
Explicit informed consent, contractual necessity, legal claims, public interest, and emergencies remain available as separate grounds. Public authorities get a restriction that goes even further in that the Minister may prescribe categories of personal data that they can never send to a third country.
Deep in Section 12 is the provision that should be getting the most attention, and it sits inside Part I, which means it goes live on January 1, 2027.
Every controller must implement a “Data Protection Management Programme,” which is a documented system of internal controls and procedures that:
The list should be read as operational rather than legal requirements: cataloged records of processing, breach identification, and the ability to find, correct, and erase a specific person’s data on request.
The 2025 amendment gave controllers one month to answer such a request, extendable by two more months with reasons. Every one of those capabilities presupposes a capability most enterprises lack: an accurate, current picture of what personal data they hold, where it lives, and who can touch it.
Section 20 also mandates Data Protection Officers for ministries and government departments, and for any organization whose core activities involve regular and systematic monitoring, special category data at scale, or processing that risks harm to data subjects. That DPO will be asking the same question the regulator will: Show me the data.
Section 18 gives every data subject the right to demand review of a decision based solely on automated processing when that decision has created or is likely to create an irreversible and continuous impact on their rights and freedoms. Profiling gets a full statutory definition in Section 56: processing that evaluates, analyzes, or predicts a data subject’s performance at work, economic situation, health, personal preferences, interests, credibility, behavior, habits, location, or movements.
The obligations keep coming from there. Under Section 24, any systematic and extensive evaluation of personal data, including profiling, triggers a mandatory personal data protection impact assessment before processing begins. Change your methodology, your technology, or your process, and Section 24(4) requires a fresh evaluation. The Authority can call in any assessment on written request under the amended Section 24(5).
Section 33(p) also empowers the Authority to make rules on the use of personal data for profiling and for automated decision-making, so expect this area to develop further as the Authority issues rules and guidelines.
For enterprises deploying AI against customer or employee data, the implications are straightforward. Every model trained on personal data, every copilot summarizing customer records, every algorithm scoring applicants becomes a regulated processing activity. You will need to know what personal data feeds those systems, prove a lawful basis for it, and demonstrate the safeguards around it.
Differentiating between AI governance and data governance will be key.
Strip away the legal language and the PDPA essentially boils down to a simple question: Do you actually know your data? Do you know what personal data you hold, whose it is, why you collected it, how long you’ve kept it, which data falls into a special category, what feeds automated decisions, and who has access to it?
Most enterprises struggle to answer these questions. Personal data is everywhere: in cloud storage, collaboration platforms, email, CRM systems, and the growing sprawl of AI tools that employees adopted without asking for approval (shadow AI).
Answering a single erasure request means finding every copy of the data, and meeting the Data Protection Management Programme (DPMP) requirement means continuously cataloging all of it.
This is what data security posture management was built for. Concentric AI’s unified AI and data security governance platform discovers, governs, and protects business-critical and compliance-sensitive data at rest, in motion, and used by AI. Powered by the Semantic Intelligence Engine’s patented language models, the platform using semantic understanding rather than simple pattern matching, so a Sri Lankan customer’s records get identified whether they sit in a database, a shared drive, or a forgotten email attachment.
The platform maps who has access to your data, flags risky sharing, and monitors the AI tools touching that data. It builds the evidence base a Data Protection Management Programme provision requires, and the same Compliance Dashboard that is already assessing your GDPR, CCPA, and HIPAA posture extends to whatever the Authority prescribes next.
PDPA enforcement arrives with the new year; data discovery, classification, and access governance take months to get right. Start now, and enforcement day becomes more of an administrative milestone than an emergency.
Ready to discover what personal data is hiding in your environment? Book a demo to see how Concentric AI can help you comply with PDPA and other global regulations.
